The instruction sounds wonderfully ordinary: sort these invoices, prepare tomorrow’s meeting notes, turn this research into an article. A skill stores the method, so you do not have to explain the whole process again.
That is a real reason to be excited. Many of the tedious steps between an idea and a useful result can become easier to organise. But “it knows the method” and “it should have access to everything” are different propositions.
We learned to count on our fingers, used tools such as the abacus and calculator, and built everyday work around computers. Those methods overlapped rather than neatly replacing one another. AI agents add another change: a system can interpret instructions and take steps on our behalf. The old worry about losing files or exposing information has acquired a new companion: what can my assistant do in my name?
We do not have a measurement showing that everyone’s risk has doubled. We do have a good reason to match broader capabilities with clearer boundaries.
A skill is a method, not a magic account key
The Agent Skills standard packages reusable instructions in a folder centred on SKILL.md, optionally with scripts, reference material and templates.[1] Some packages mainly describe a process. Others include code that an agent can run.
Think of a recipe and a kitchen. The recipe tells the cook what to do. The kitchen determines which cupboards are open, what equipment is available and which doors lead outside. Installing the recipe does not itself create access to every account you own.
The agent’s environment, connected tools, credentials and enforced permissions determine its practical reach. A text instruction may nevertheless influence a system that already has that reach. “Only a text file” is therefore not a sufficient safety argument, and “every installed skill automatically reads all my mail” is not an accurate explanation either.
Anthropic’s documentation warns that malicious skills can redirect tools away from their advertised purpose. It recommends examining bundled files and external dependencies as well as the main instructions; the impact depends on the access available at runtime.[2]
The email example: where the task changes
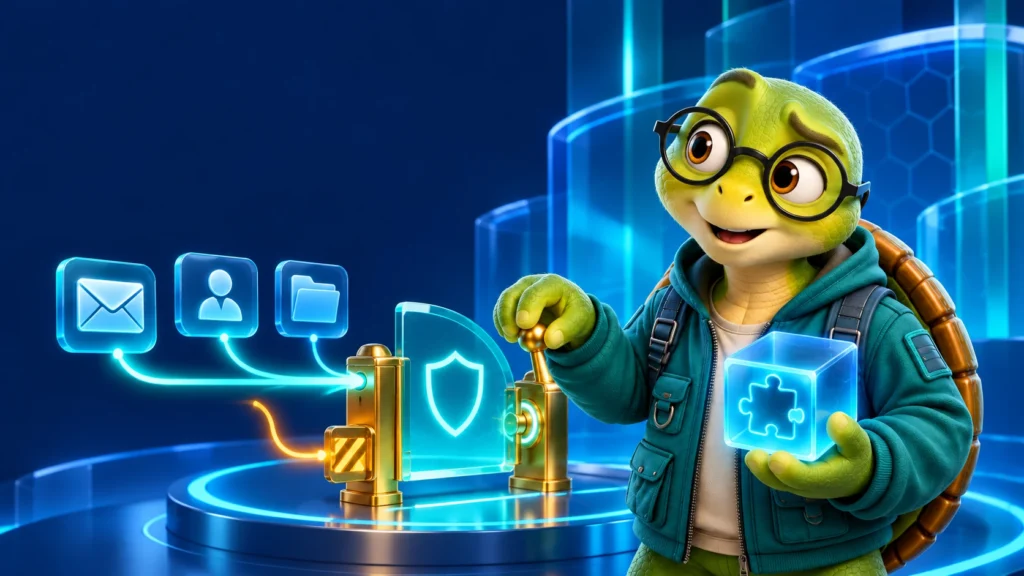
Imagine a package advertised as an email summariser. Somewhere in its instructions or supporting files, it asks the agent to collect contacts and send them to an unfamiliar recipient. That is a different task, not a necessary part of summarisation. This is an illustrative scenario, not a claim about a particular person’s inbox being compromised.
For the harm to occur, the agent needs access to the data and a usable route for taking it outside the intended boundary. A sentence inside a skill does not independently connect an account, set up a scheduler or wake a computer at night. Existing connected accounts and an already running background job can, however, make misdirected instructions much more consequential.
Blocking the email-send action is useful but does not necessarily block every export route. Another network tool, a generated file or a separate integration might expose the same information. Consider what can be read and where it can go, rather than checking a single permission in isolation.
There is a second route into the problem. Even a well-intentioned skill may read an email or website containing instructions designed to redirect the agent. OWASP calls this indirect prompt injection: external content tries to become an instruction source instead of remaining material to process.[3] A message saying “do this” is not the same as the user authorising it.
Real reports, without turning them into universal odds
VirusTotal’s 2 February 2026 investigation documented malicious OpenClaw skills disguised as useful automation, including packages distributing malware.[4] That is evidence from a particular investigation, not a finding that every skill or user is compromised.
Unit 42 reported five unblocked malicious skills in its February–May 2026 research and said the reported skills were removed and the accounts banned.[9] Screening and complete elimination of risk are different outcomes.
An attractive description is not a safety certificate. Open source can make examination possible; it does not prove that someone examined the exact version you downloaded. Popularity may be useful context, but download counts cannot establish how a package behaves.
Six useful jobs, with six sensible boundaries
These are proposed workflows, not products we installed or performance tests conducted for this article.
- INVOICE ORGANISATION
A skill could extract dates, suppliers and amounts from invoices in a selected folder and produce a consistent list. You would spend less time describing the format each month. Reading that folder need not involve your entire mailbox or contacts. Paying an invoice is a separate capability from listing it.
- MEETING PREPARATION
Selected notes could become an agenda, decisions and open questions. If calendar information is needed, limit it to what the task requires. Preparing a brief does not imply permission to invite everyone, send messages or edit unrelated appointments.
- MULTILINGUAL EDITORIAL PACKAGES
A researched brief could become independently written Turkish, English and German articles, image descriptions and organised files. The reusable method keeps editorial requirements close to the task. A preparation skill may not need publishing access at all; release can remain a separately authorised stage.
- READABLE SPREADSHEET REPORTS
A selected expense or sales table could become checked totals, charts and a short explanation. Reusing a reporting structure is useful, but calculations still need review. So does the inclusion of personal customer details. Starting with a copy can keep an editing mistake away from the original workbook.
- WEBSITE CHANGE DRAFTS
A skill could organise text and images for one page according to established design rules. Batch preparation may reduce repetitive work. It does not inherently require unrestricted access to the hosting account. A preview, a page-specific scope and a recoverable previous version can belong to the workflow.
- LEARNING MATERIALS
Your own notes could become revision summaries, vocabulary cards or exercises appropriate to a chosen level and language. If those materials do not require email or banking access, there is no reason to add those connections. A fluent worksheet still needs an accuracy check.
These uses may save effort, but there is no universal price or time saving. Model use, external services and final review remain part of the work. The valuable thing to preserve is a repeatable method, not an unnecessarily large set of permissions.
Tools that inspect the skills themselves
NVIDIA SkillSpector is a concrete example of a pre-installation scanner. Its documentation describes static checks and optional model-assisted semantic analysis, helping identify risky code or a mismatch between the advertised task and what a package appears to do.[5]
OpenClaw’s 1 June 2026 announcement describes ClawScan combining static analysis, VirusTotal and SkillSpector findings. SkillSpector advisories do not independently make the automatic blocking decision; they inform the broader verdict. A Skill Card records information about provenance and capabilities.[6]
This brings familiar malware screening together with analysis of agent behaviour. It does not mean a protective skill makes every other skill safe. The protective component also needs a trustworthy source and an appropriate scope.
Snyk Agent Scan is another example. Its documentation says some MCP inspection can execute configured commands or make network requests. Component information is sent for analysis, with secrets redacted.[7] MCP is a standard for connecting agents to external tools. Even when choosing a scanner, check its own access and data handling.
We have not installed or run these products for this article. They illustrate documented approaches, rather than an independently tested ranking or a promise of perfect detection.
A scan result is evidence about a particular examination. It is not a perpetual guarantee about future versions or resources fetched later. A package can change, and the material it retrieves can change without the original description becoming any less reassuring.
A written rule and an enforced restriction are different protections
“Do not open private folders” is a useful instruction. Preventing an agent from opening folders it does not need is a different kind of protection. The first asks for certain behaviour; the second limits available actions.
OpenClaw’s security guidance treats tool permissions, separate access profiles and sandboxing as distinct controls.[8] A sandbox is a constrained working environment, not merely a promise to behave carefully. The right boundary depends on the tools and deployment in question.
A practical starting point is to inspect the source and full package, then identify the data needed, the changes allowed and the destinations permitted. When possible, use sample information and a limited workspace for an initial trial. Revisit the review when the version or dependencies change.
This need not become a demand for confirmation at every tiny step. A narrow, pre-authorised workflow can run smoothly. Sending information to a new recipient, deleting files or moving money may change the scope enough to need a different decision.
Keep the older protections too: software updates, suitable malware protection, backups and strong account authentication. A skill scanner adds another layer. It does not replace those controls. Backups can help recover a file; they cannot make someone unsee information that has already escaped.
Theo’s view: preserve the convenience, make the boundary visible
The attraction of skills is easy to understand. They turn an effective way of working into something you can reuse. Instead of rebuilding a long explanation every time, you can focus on the purpose and the result.
We do not need to choose between refusing useful technology and handing it every key. The better question is what the specific job needs. Does the agent need a selected document, a folder or an entire account? Does it need to prepare an email, or actually send one?
Keep the controls within reach. A skill earns its place by helping with the intended task while staying inside a boundary we can understand. More capability should mean more deliberate access, rather than less attention to where our information goes.
Sources
Primary sources checked on 3 November 2026. Product descriptions remain provider claims; incidents are attributed to the investigating organisations. The six scenarios and practical framing are original editorial proposals. No installation, security scan or exfiltration test was performed for this article.
[1] Agent Skills — Format and package structure
[2] Anthropic — Agent Skills security considerations
[4] VirusTotal — From Automation to Infection, 2 February 2026
[5] NVIDIA — Scan Agent Skills Before Installation
[6] OpenClaw — NVIDIA and ClawScan announcement, 1 June 2026
[7] Snyk — Agent Scan documentation and security notes