According to Binance’s initial report of November 3, attackers used a compromised employee computer and an internal AI tool to reach other devices. They later reached a service that authorizes wallet transactions. Binance says approximately $6.34 billion in digital assets was affected.
How the access chain developed
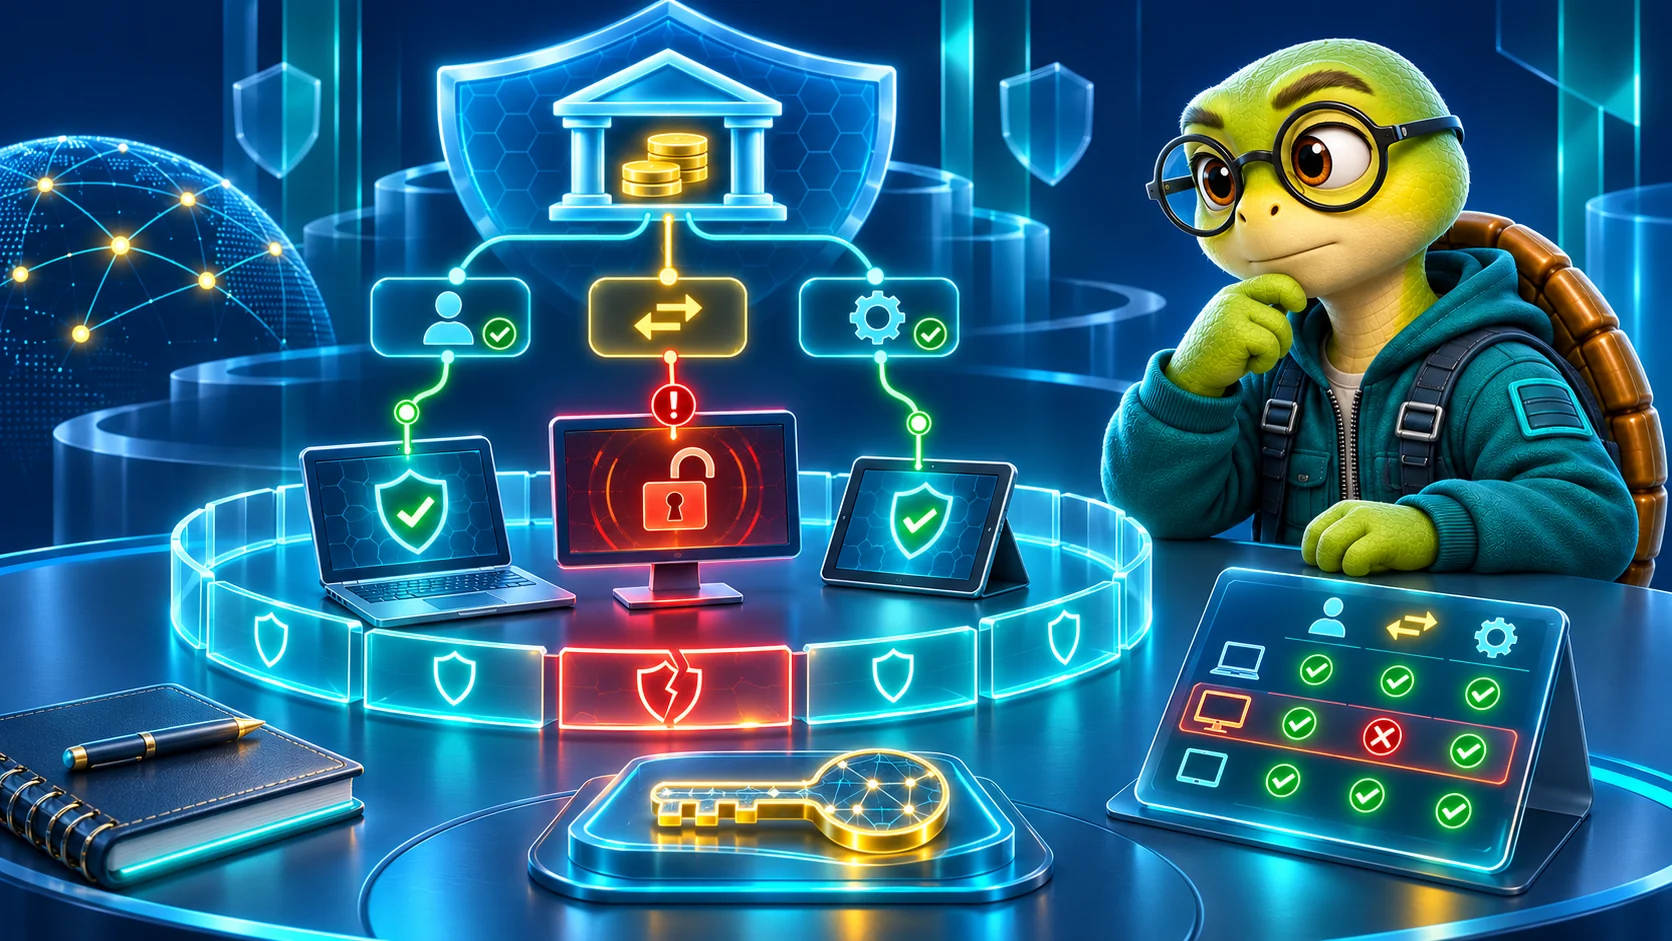
Binance describes a campaign that unfolded over months. In September, a software engineer went through a fraudulent recruitment process and downloaded an assignment containing malicious code onto a work computer. On October 20, the company says, the attackers used that computer and an internal AI tool to gain control of two other engineers’ devices. A deployment permission token was found on one of them.
On October 29, stolen credentials helped the attackers reach the wallet signing service and initiate transactions outside the ordinary withdrawal process. Binance has not explained the precise technical actions performed through its AI tool. Its report identifies the tool’s place in the chain; it does not establish that the AI model itself had a vulnerability.
What Binance says happens next
In its November 3 update, Binance said roughly $2.85 billion in assets had been frozen or intercepted, subject to reconciliation and changing market prices. The company says it will bear the loss rather than pass it to users. It also reported that, by October 31, 98% of the affected token assets had been replenished.
Binance says it rebuilt the affected wallet system and internal AI tool, replaced devices and decommissioned related credentials. The investigation continues, with an independent security review planned. For teams using connected AI tools, the case makes the boundary around device access and deployment permissions a practical question to examine.