OpenAI says it used an upcoming cyber model in a controlled study of Linux kernel vulnerabilities. In its November 4 publication, the company said the pipeline reproduced 1,724 vulnerabilities and generated 948 working local privilege-escalation proofs of concept.
What the numbers represent
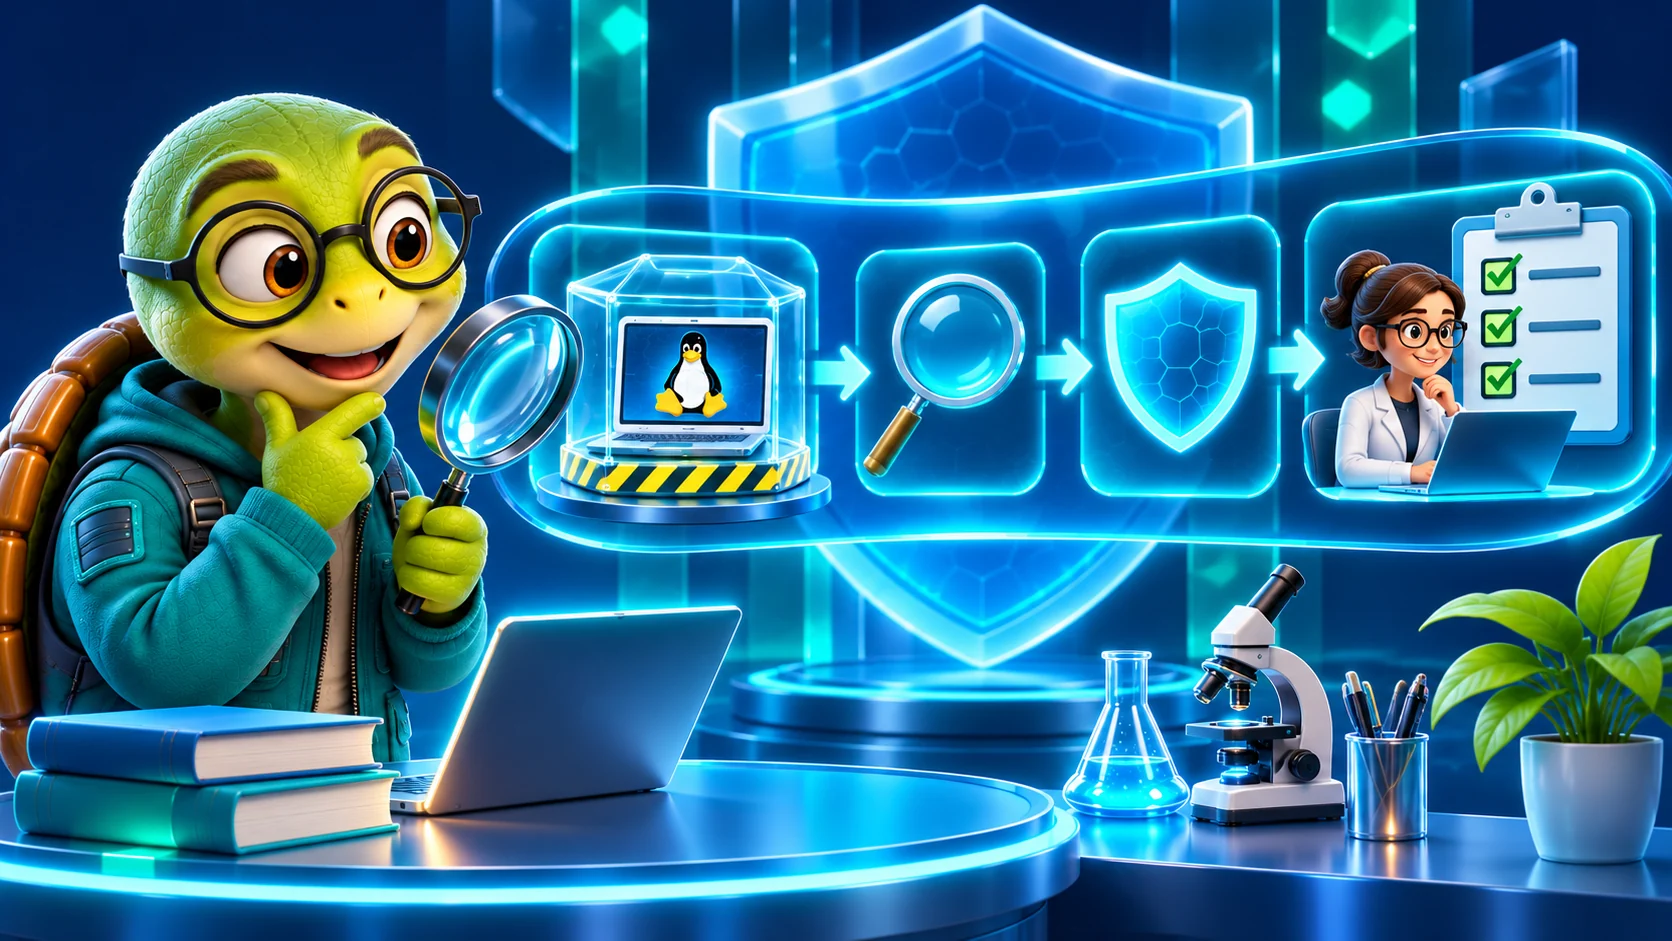
The system first analyzed 2,308 candidate findings. It then attempted to reproduce them in isolation, assess their impact and prepare candidate patches. Human security researchers reviewed the output and reported findings to maintainers.
Local privilege escalation means that someone who already has limited access to a machine can obtain higher privileges. The 948 figure counts working examples in this controlled run. It does not mean every Linux system was remotely compromised or that every proposed patch has been deployed.
Review and cost
OpenAI reported $1,213,430 in API costs for the mid-October run. Following guidance from Linux maintainers, it says it began reporting the most critical findings and continues working on reports and patches. Some issues had already been patched or were being publicly discussed by other contributors while the scan ran.
The study shows how vulnerability research may be scaled, while a candidate fix still needs review before it can be trusted in production. Keeping systems updated and maintaining isolation between components remain separate defensive layers.