A managed authorization option for Claude connectors aims to spare teams from connecting each supported service one person at a time. An administrator can configure access for an organization so eligible members receive it when they first sign in.
Two ways to establish identity
The Claude help centre says the feature is available on Team and Enterprise plans. One route uses an organization’s identity provider and single sign-on across Claude and the connected service. The other lets Claude send a signed assertion identifying an organization member to a supporting connector.
Claude-issued authorization is in beta. It does not require an identity provider or SSO, but the service must support it, an administrator must establish trust with that service, and the user’s email addresses must match.
Automatic connection still has boundaries
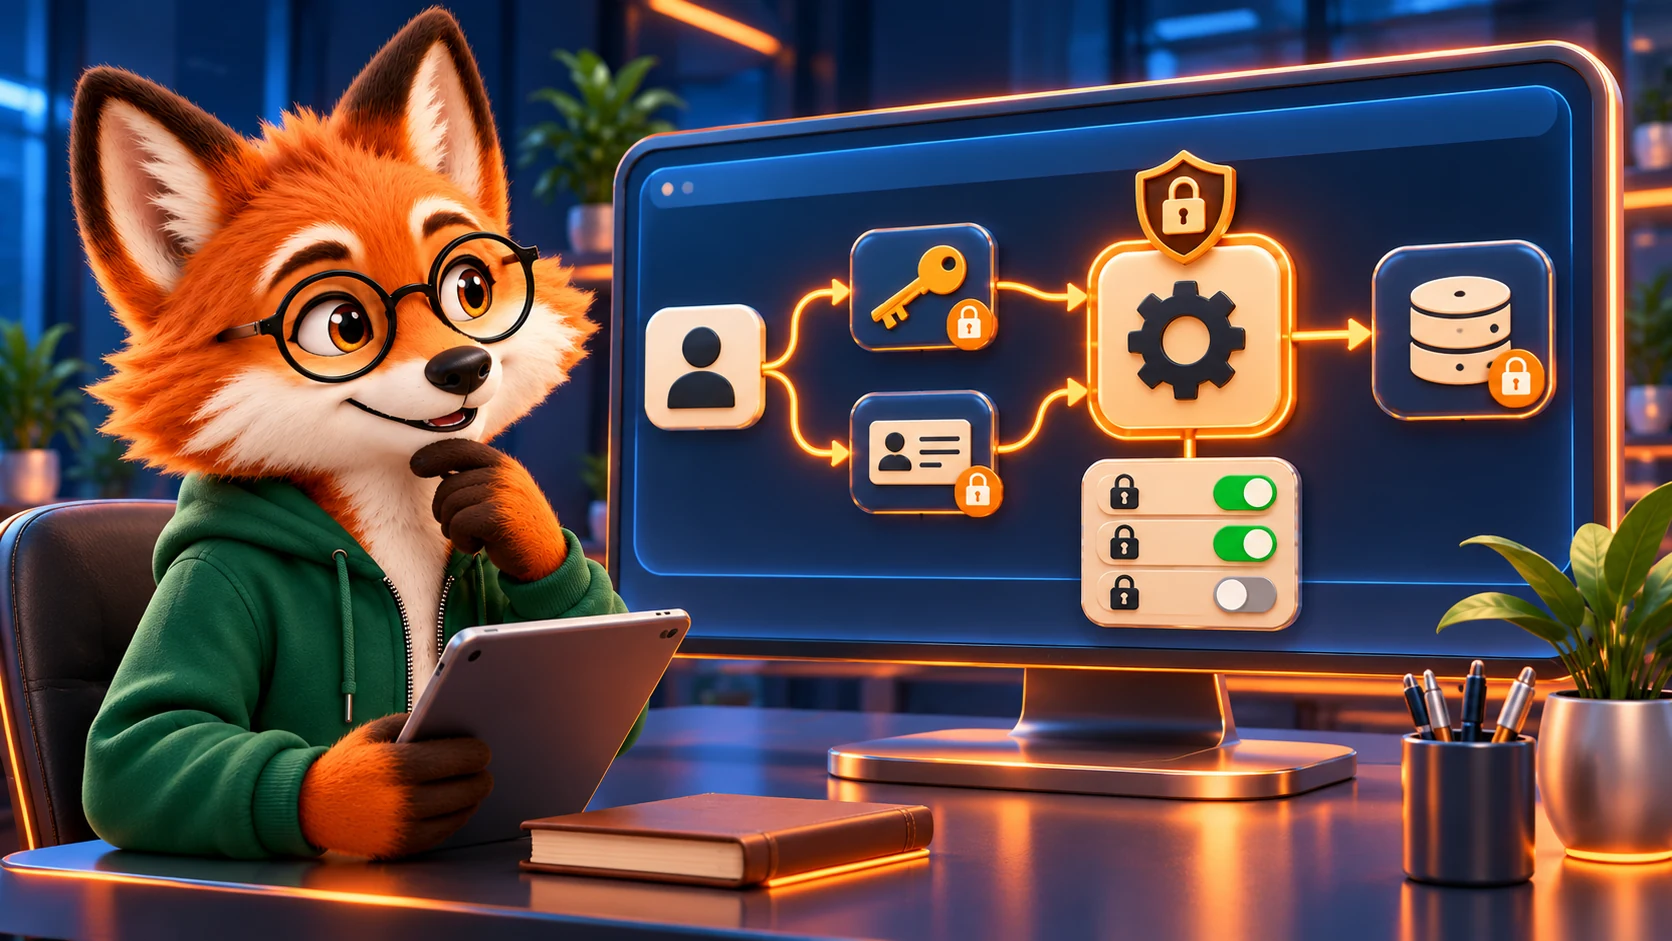
Administrators choose which connectors and roles receive access. Anthropic says Claude checks organization membership for Claude-issued authorization; it does not itself verify the connected service’s own sign-in rules or multi-factor authentication. The service’s permissions and administrator settings therefore remain part of the setup.
For example, Supabase says members use their existing Supabase permissions under its managed MCP connection. Support and setup requirements differ by connector, so check the provider’s instructions before enabling one.